
We audit your website, fix it, or build it correctly from the ground up.
WebTrustEngine measures security, accessibility, performance, SEO, structured data, privacy and AI readability readiness. It delivers a leadership-ready report, actionable fixes and a verified website through one evidence chain.
Every finding arrives with file-level evidence: leadership reads the report, your technical team verifies the annexes.
- I have a website but do not know its conditionWebsite Audit and Executive ReportWe examine your URL or site package and deliver the risks, affected pages and business priorities as a clear executive brief, detailed technical annex and prioritized action plan.Request a website audit →
- I have a website and want its problems fixedExisting Website ImprovementWe prioritize the audit findings, complete the applicable fixes on a safe working copy, rescan the website and prove the before-and-after result.Improve my existing site →
- I need a new websiteNew Website Design and DevelopmentWe design and develop a fast, accessible and secure website aligned with your brand and business goals, prepare it for SEO and AI visibility, and verify the delivery with the engine.Plan my new website →
See what the audit produces: a sample executive report from a real run →
PRODUCT OVERVIEW
See where your website stands and decide what comes first
Detailed reading
WebTrustEngine examines your live website, your site archive or your local files. It brings the technical findings, the measurement gaps and the work to be done together in one place. The result is reporting leadership can decide on and an improvement plan your technical team can actually carry out.Measurement status is a separate indicator from the score: it states how many checks could be measured. Detail
Explore the audit service · Read the product guide
Live URL, ZIP and local-folder input · Executive report with technical annexes · Optional controlled improvement
Choose the starting point that fits your need
I want to know the condition of my website
See which problems come first, where further measurement is needed and which jobs your technical team can pick up straight away. Assess your current site, its state before a redesign, or the files your agency delivered.
I want the problems on my existing site fixed
Turn findings into work that can be carried out. The applicable fixes are prepared on a separate working copy; you review the changed files, the re-measurement results and the rollback records together.
I want to develop a new website
Start from static site candidates built on your brand and content material. Review the page structure, the design and the technical readiness together, and settle the content migration, the integrations and the launch work up front.
New website design and development
What you have at the end of the audit
A decision brief for leadership. We gather the site's current condition, the priority findings, the measurement gaps and the recommended order of work into one narrative, so you can see the basis for allocating resources.
Actionable work for the technical team. Each finding reads as one unit: the affected pages or files, the observation behind it, the suggested action and the condition for retesting. We keep problems that spread through a shared template separate from one-off fixes.
Evidence you can inspect. We record which input, method, environment and date produced each result. Where the reporting flow allows it, we bind the Word and PDF documents, the technical records and the delivery-verification data to the same piece of work.
A way to judge what changed. We place the next audit alongside the earlier state with a comparable scope. Closed findings, new problems and the areas that could not be measured all stay visible.
Audit your website across domains that complete each other
| Domain | The decision the audit helps you make |
|---|---|
| Technical SEO and content | Which work comes first in page discovery, links, titles and content structure? |
| Structured data and organizational identity | Are your organization, service and page details presented in a form machines can understand? |
| Security and infrastructure | Which security signals do your public responses and the supplied files carry? |
| Performance and resource use | What loading and browser behaviour on the audited pages needs improvement? |
| Accessibility and usability | What do the automated checks show, and which user tasks need separate assessment? |
| Mobile rendering and media | How do content, images, interaction targets and page layout behave in the selected viewport? |
| Privacy and third-party data | What storage and request behaviour was observed, and which further data would complete the assessment? |
| Project and change tracking | What changed in the new release, and which work needs auditing again? |
In the report we collect the topics in this table under the 10 domain headings further down this page. Which measurements actually run depends on the selected scope, the input, the tools and the data provided. The full feature index, the methods and the prerequisites live in the product guide.
Read the capabilities and their operating conditions
How the work proceeds
- We set the goal and the scope. Together we define the site address or the files, the purpose of the assessment, the page limit and the required measurements.
- We run the audit. The engine executes the applicable checks and records both the findings and the measurement gaps.
- We translate the results into decision language. We report the site assessment, the priorities, the need for further review and the technical work.
- We prepare the selected improvements. Where they are in scope, we apply the applicable SafeFix operations on the working copy; the remaining work goes into the relevant team's implementation plan.
- We measure the change again. We examine the effect of the fix and any regressions. Applying it to the live site and the decision to publish remain the responsibility of the authorised team.
If the fix scope is agreed at the outset, the engine can apply the applicable operations within the same run after the first analysis and re-check them before the final report.
From one finding to finished work
Suppose a form field is missing its accessible name. The audit points to the affected page and to the element itself. The technical team sets the right label; the re-check then assesses whether that same element meets the expected condition. Where more is needed to show that the form can be completed, the keyboard and assistive-technology tasks are examined separately as well.
Every technical sub-check is assessed together with the scope of the user task it belongs to.
Control over your data and your changes
WebTrustEngine works local-first. An offline ZIP or folder audit works only from the files you supply. Active security testing requires written authorisation and a separate scope document. The data requirements of any external services and additional measurements you choose are settled along with the scope.
A standard audit changes no source file. When you select SafeFix, we prepare the edits on a separate working copy. Decisions about content, design, integrations and going live stay with the people responsible for them.
What you may want to know before starting
Can a site that is not live yet be audited?
Yes. A file-level audit can run from a ZIP or a local folder. Live server, redirect and link behaviour is measured separately, once a suitable production or preview environment is available.
Does the audit fix every problem automatically?
Analysis and fixing are separate scopes. SafeFix can prepare the supported edits on a working copy once the information it needs is supplied. Content, infrastructure and application-development work is planned separately.
How should a high score be read?
Read a score together with the model used, the scope actually measured and the open findings. We show the areas that could not be measured, and the human judgements the remaining risk requires, separately.
How long does it take, and how is it priced?
Site size, the number of languages, the measurement scope, data preparation and the implementation needed determine the work plan. Duration, fees, support and delivery terms are settled on that scope.
Choose your first step
To learn where you stand, start with the audit scope. If you already hold a list of findings, look at the improvement process; if you are building something new, look at the design and development scope.
See the audit scope · See the improvement process · See the new-site scope
WHY GOVERNANCE?
The web is no longer a one-off project
Detailed reading
A website is now a human storefront plus a machine surface.
The page a visitor sees is simultaneously the input of dozens of automated readers. A page flawless for humans can carry missing headers, broken schemas and unclear identity signals for machines.
Even with great design, machine readability can be weak. Visual redesign projects rarely touch the meta layer, security headers or structured data; the site looks new while its audit surface stays old.
WHO USES IT
Who uses it, and when?
Four typical moments: an evidence-based snapshot before a corporate site renewal; independent acceptance of an agency delivery; a recurring governance round; and quick due diligence before a merger or transfer.
Detailed reading
WHAT IS R50?
Every published figure — counted from code
Detailed reading
R50 is WebTrustEngine's public capability set. Its distinguishing trait is number discipline: every published figure is counted from code.
Claim safety
Every published claim is tied to code and an evidence file.
FOUR MODES
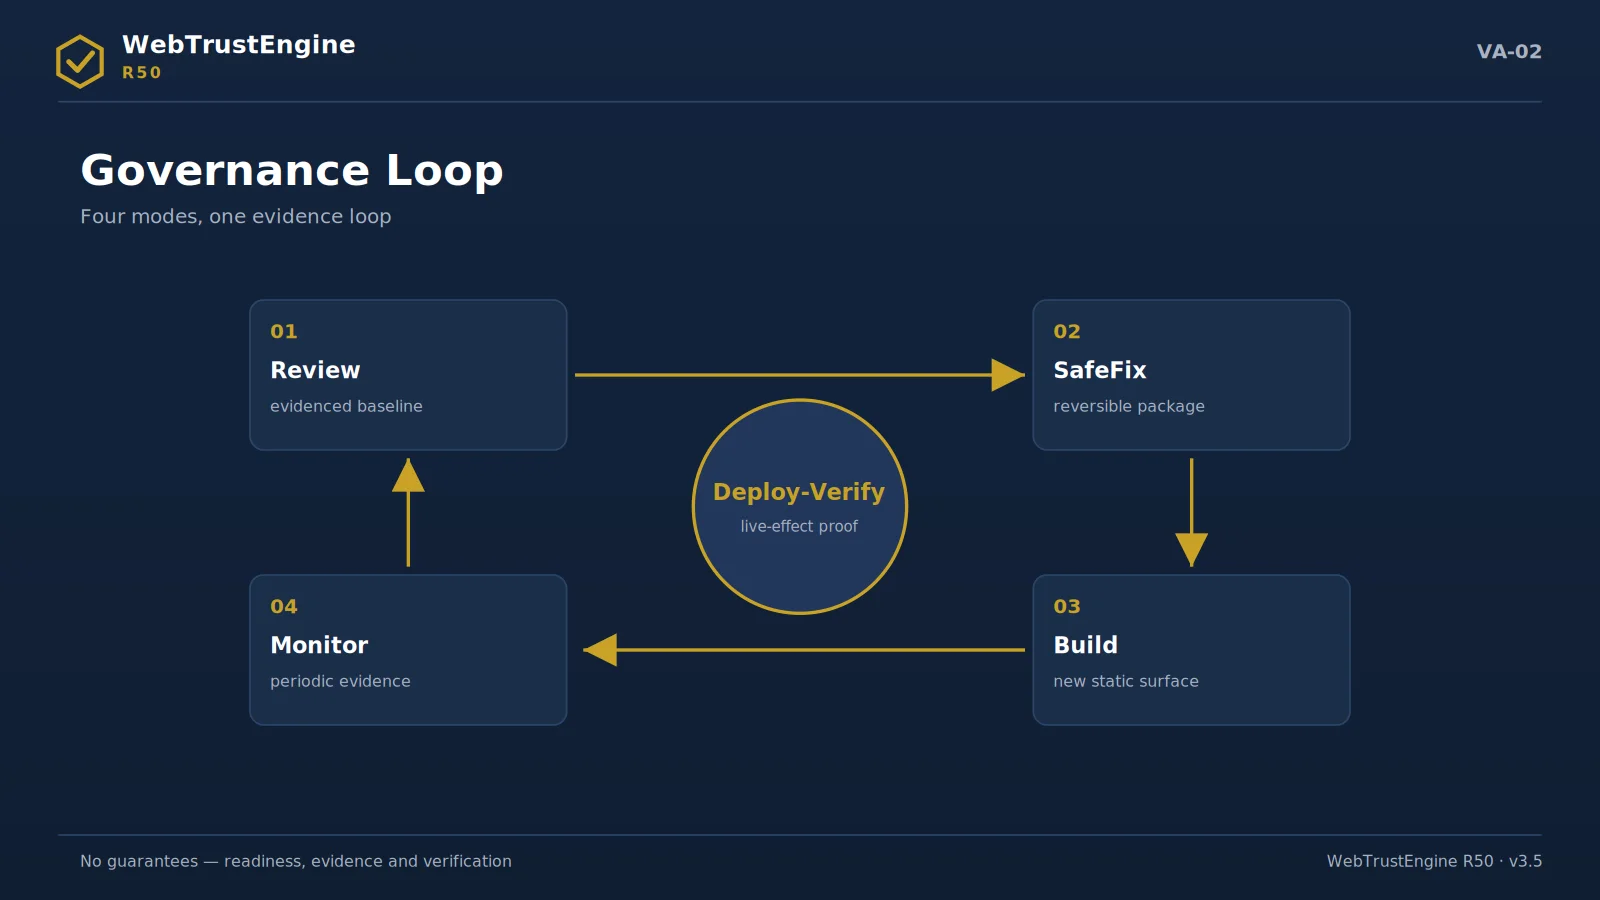
Review → SafeFix → Build → Deploy-Verify
Each mode produces its own evidence; no mode issues a live pass.
Detailed reading
Review
An evidenced baseline without touching a file: a score computed from eight scoring categories, plus findings classified across 10 domains.
score + findingsSafeFix
Low-risk fixes in a working copy; every change is written to a manifest.
fix manifestreversibleBuild
A schema-ready static surface: meta, canonical, hreflang, JSON-LD, accessibility skeleton.
static surfacereversibleDeploy-Verify
We pull live headers after upload and run the independent-tool recipes.
live proof
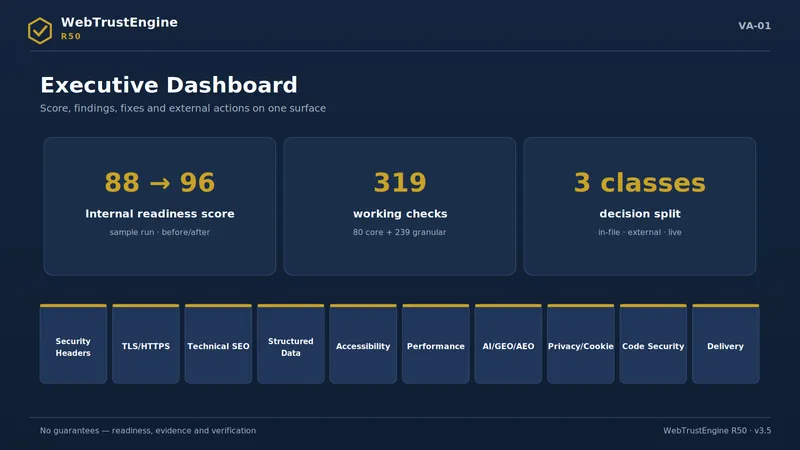
The 10-domain audit and reporting model
We report findings under these ten headings. The overall score comes from the engine's eight scoring categories. Each domain's one-line scope follows; evidence, sample findings and boundaries live on the Score Model page.
Security Headers
HSTS · CSP · nosniff
TLS / HTTPS
encrypted transport
Technical SEO
meta · canonical · sitemap
Structured Data
JSON-LD identity
Accessibility
alt · label · heading
Performance
static readiness
AI / GEO / AEO
readability
Cookies
tracker visibility
Code Security
secrets · exposure · patterns
Delivery
deployment hygiene
Detailed reading
SAFEFIX
Not a rebuild — a safe improvement
Detailed reading

The evidence package: files, not a score
We deliver the changed-files list, the rollback manifest and the before/after score together. Every change reverts in a single step.
See the processChanged filesFlat list of every touched path.
FIX_MANIFEST.jsonPer-file before/after hashes.
ROLLBACK_MANIFEST.jsonThe single-step way back.
DEPLOY-VERIFY
Producing files is not enough
Upload, cache purge, live header pulls and independent-tool recipes: we complete the evidence in production.
Detailed reading
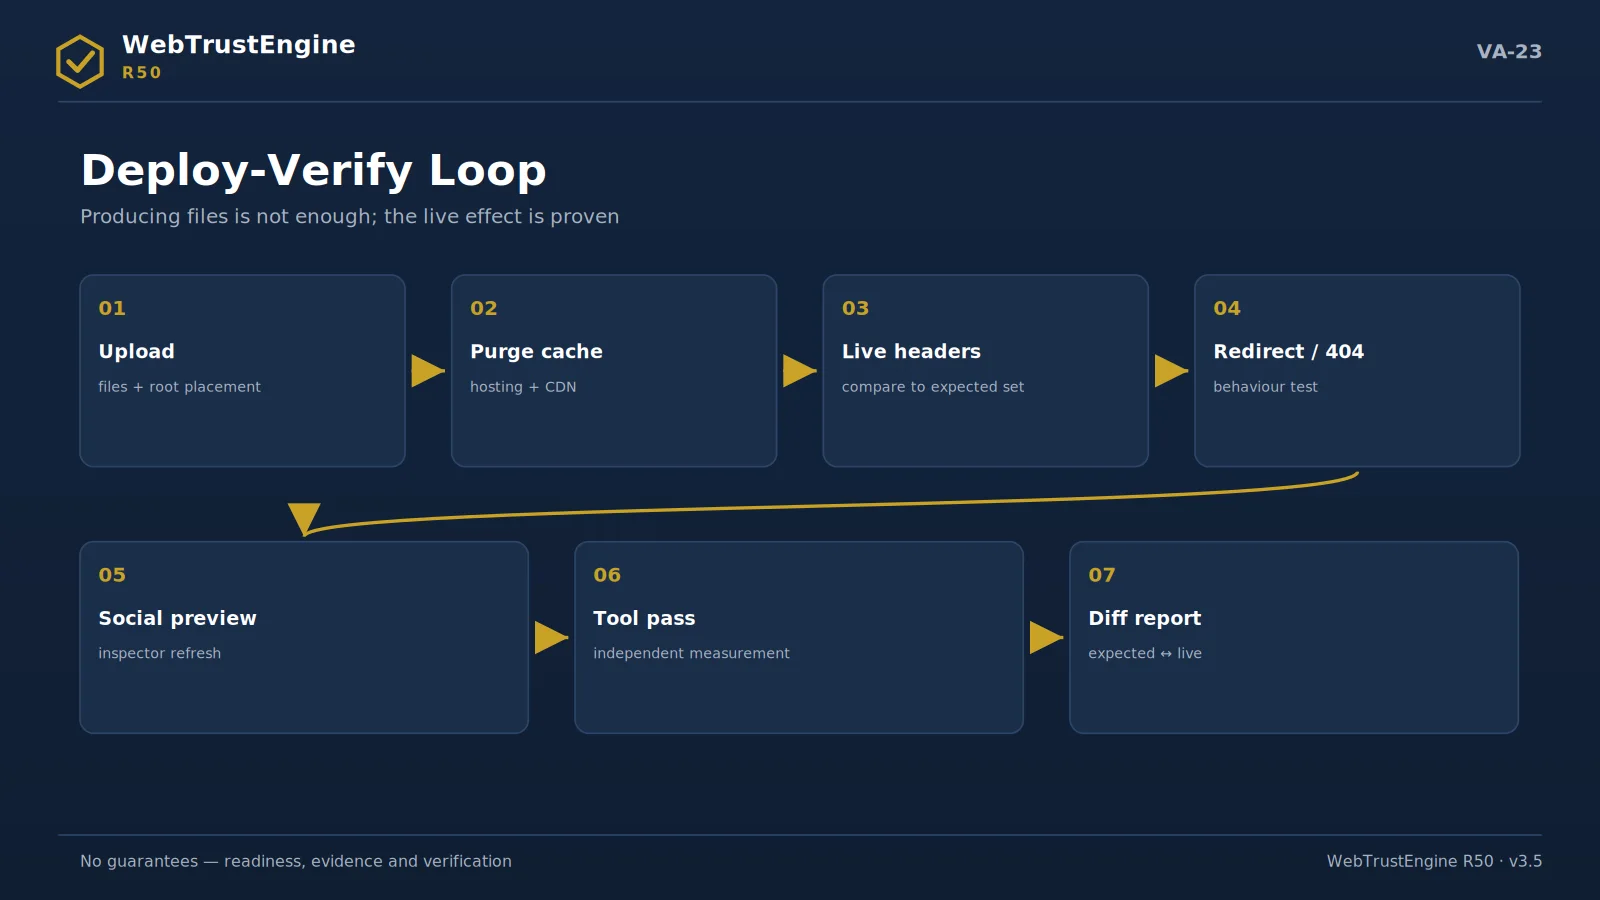
- Live header pull
- robots/sitemap live
- OG card refresh
- Search Console submit
- SSL Labs run
SECURITY BOUNDARY
Security review with no attack attempt — the boundary is in writing
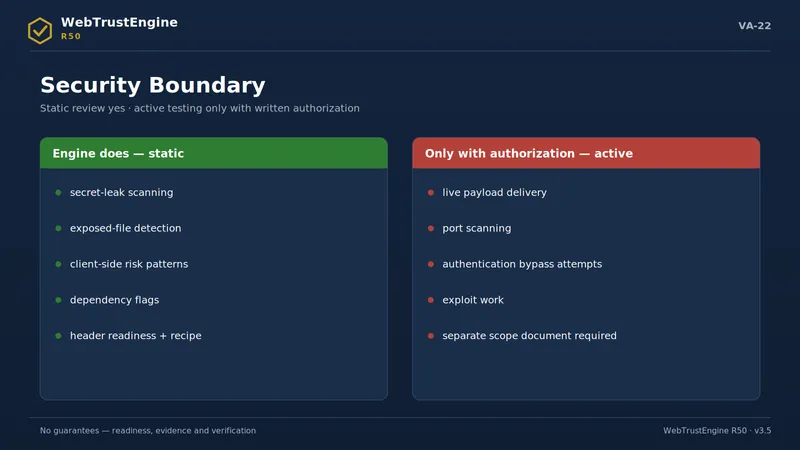
In short: in an offline ZIP or folder audit the engine sends no requests to your site and looks for security signals only in the files you supply; in a live-URL audit it sends only passive, read-only requests to the target you designate.
A static security review is security analysis over source, configuration and output files without touching the target system. WebTrustEngine's security layer stays within this definition and has four blocks: secret scan (key/password/token leakage), exposed files (.env, backups, .git, config exposure), client-side risky patterns (eval, document.write, dangerous sinks) and server-side SAST classifications (SQLi/command/traversal/deserialization/SSRF/XXE markers).
SCA/CVE logic accompanies these: we flag the risky ranges of known library versions and bind each flag to an update recipe. CSP/HSTS readiness and OWASP mapping put findings into a shared language.
This product is not a penetration test. Any DAST-class behaviour requires written authorization, ownership verification and a separate scope document. So you know exactly what you bought and what must be ordered separately.
Boundary glossary — what does static scanning cover?
- secret scan
- exposed files
- JS sink patterns
- SCA/CVE flags
- CSP/HSTS readiness
- OWASP mapping
- DAST = authorization + scope
Boundary
Active testing requires written authorisation; the engine offers static security review.
Get an evidenced snapshot without touching a single file.
Prepare an audit requestVISUAL SYSTEM
Detailed reading
The brand speaks its own visual language



Brand Center: 32+32 visuals, 24 banner sizes, logos →
Critical questions — quick answers
Detailed reading
Q: How do we start?
A: You share your site address or a site package (ZIP); the first review produces an evidenced snapshot. We set the scope and the schedule on that snapshot.
Q: What is delivered?
A: An executive brief plus a technical-annex report (DOCX/PDF) and a machine-readable evidence pack: changed files, manifest, checksums, rollback plan. Scanning and reporting are automated.
Every file in the evidence pack, explained in the Evidence Hub
Q: Why is there no price on the site?
A: Quotes follow scope: one site or a multilingual estate, with or without live verification. A fixed list price is therefore not published.
Q: What can it see without touching the live site?
A: All in-file signals in ZIP/local input: meta, schema, header readiness, accessibility markers, static security patterns.
Q: ZIP vs live-URL analysis?
A: ZIP shows file truth; live URL shows response truth; headers and redirects finalize only live.
Q: What if the site breaks after SafeFix?
A: The rollback manifest reverts in one step; the backup dir ships in the package.
Q: How is the rollback manifest used?
A: Copy files back from the backup dir; the changed/created lists guide you.
Q: Which changes are the owner's commercial call?
A: Meaning-changing content, brand/voice preferences and legal text are commercial decisions; the live publish decision also belongs to the owner.
Q: Why are the figures never summed?
A: Checks, patterns, bridges, fixers and recipes count different kinds of work; different units are never merged into one total.
Q: How is the 348 figure counted?
A: Counted from code by the CLI; the quality check and the release record report the same figure.
WHY WEBTRUSTENGINE?
Quick preview: against the four closest products
Detailed reading
These four points are what make the difference in an evidence-bound decision file. The full table is 12 products × 16 capabilities on a separate page; every competitor cell is bound to an official product page.
- URL, ZIP and local-folder input — we found no equivalent on hosted crawlers.
- Hashes, manifests and number provenance — the same input yields the same number.
- Reversible fixes with a rollback manifest.
- Local, controlled data processing.
Ready for the first review?
Get an evidenced baseline without touching a file. Send your request through the topic lanes on the contact page and we will settle the scope and the quote together.